Table of Contents
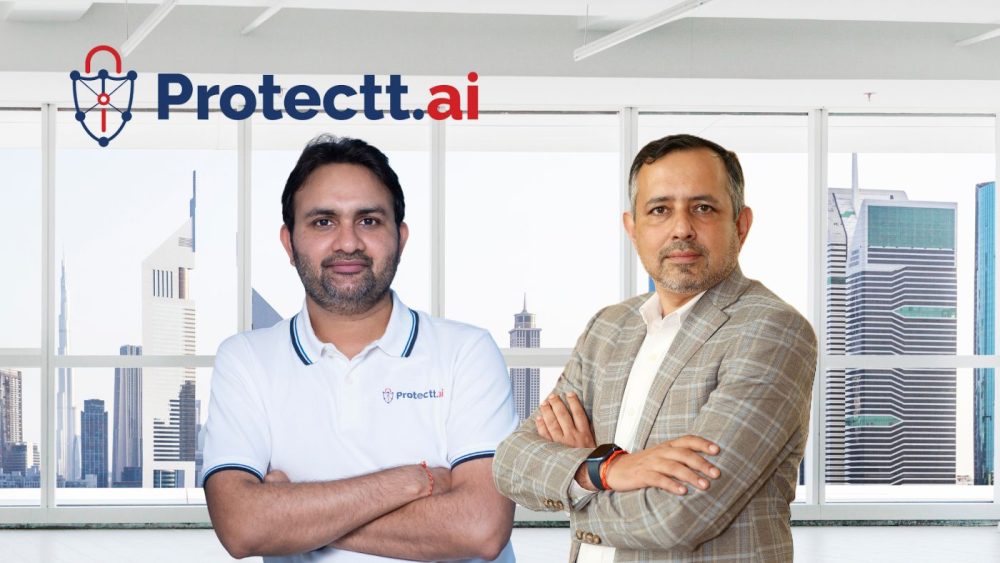
Protectt.ai builds security that sits inside mobile banking apps and watches the device and the live session, not only the login. Manish Mimani founded the Mumbai-based company in 2020 after working as a global chief information officer, and Pushkar Singh is its country head for the Middle East and Africa.
The company says it covers more than 900 million unique devices and safeguards more than 10 billion app sessions a month, and it launched a new version of its AppProtectt platform in Dubai in February.
The questions came as UAE banks face mobile malware pressure. Security vendors say the Central Bank of the UAE issued Notice No. 2176.2026 in April on malware affecting Android devices, and summaries of it describe requirements around threat detection and runtime protection.
The CBUAE’s own text wasn’t checked for this piece. Separately, the chairman of the UAE Cybersecurity Council, Mohamed Al Kuwaiti, said the country recorded about 640,000 cyberattacks on one day, 15 September, after nearly 800,000 a day in April.
Key Takeaways
Manish Mimani says an increasing share of mobile fraud happens inside an authenticated session: a customer installs a remote-access tool, grants accessibility permissions or interacts with an overlay, while the credentials, device and session all look genuine to the bank.
Pushkar Singh says the UAE’s 640,000 cyberattacks figure measures the national threat environment across sectors and not mobile banking fraud, and that banks need to be able to warn, verify, block or end a risky session as it happens.
Asked what would show the GCC expansion working, Mimani points to existing regional clients, which Protectt.ai can’t name, scaling in production. Singh points to a live customer deployment in at least one more GCC market.
The Interview
You founded Protectt.ai after seeing, as a global CIO, how mobile banking apps had become the primary attack surface for fraud. What was the specific moment or incident that convinced you this needed to be its own company?
Manish Mimani: The decision came from seeing the same gap repeatedly in my CIO roles. Banks had strong controls across their data centres, networks and authentication, while more of the customer journey was moving onto a phone the bank did not own or manage.
The bank’s front door had moved onto the customer’s device, but security visibility had not moved with it.
In the fraud situations I was seeing, the bank’s systems could behave as expected. The credentials could be valid, the device recognised and the session genuine, while the customer’s device or live journey had still been compromised.
Security teams could confirm that an application had passed testing before release but had far less visibility into what was happening while it was running on the customer’s phone.
That recurring operational gap convinced me that mobile banking needed protection inside the application and throughout the live transaction.
The application, device and session had to be assessed together. Protectt.ai was created to close that gap at the scale required by mobile-first financial services.
Also, read Upcoming UAE Fintech Events in 2026: What’s Still Ahead
Protectt.ai now covers more than 900 million unique devices and has safeguarded more than 10 billion app sessions monthly. What’s the one attack pattern you’re seeing at that scale today that you weren’t seeing two years ago?
Manish Mimani: One of the clearest shifts is the combination of several techniques inside an authenticated customer session. Attackers may persuade a customer to install a remote-access or screen-sharing tool, grant accessibility permissions or interact with an overlay that imitates part of the banking journey.
The transaction can then be observed or influenced within the legitimate application, on a recognised device, while the real customer is present.
That creates a difficult picture for conventional controls. The credentials may be valid, the device familiar and the behaviour broadly plausible.
Runtime security adds the context needed to identify whether a remote-control channel is active, an overlay is sitting on the payment screen or accessibility services are driving the input.
At the scale we monitor, these techniques are increasingly combined and automated. AI is also making the surrounding social engineering faster and more convincing.
This is why live device and session intelligence has become central to mobile fraud prevention.
You’ve said India’s digital finance ecosystem needs a security architecture built around its mobile-first, UPI-driven environment rather than adapted global solutions. Does that same logic apply to the UAE’s Aani instant payments and Jaywan card scheme, or does Gulf mobile-first banking need a genuinely different approach?
Manish Mimani: The core security principle applies in both markets, although the implementation has to reflect how each ecosystem works. India has given us experience protecting mobile payments at extraordinary scale through UPI.
In the UAE, Aani is accelerating instant account-to-account payments and Jaywan is strengthening the domestic card ecosystem.
As transaction speeds increase, banks need to understand the state of the application, device and session before a payment is authorised.
The architecture can remain consistent: protect the application, assess the device and evaluate the live transaction.
The detection logic then needs to reflect CBUAE requirements, UAE payment journeys, customer behaviour and the operating models of regional banks. Threat signals and response thresholds also need to be tuned for the market in which the application operates.
Our experience in India provides a strong technical foundation.
Our Dubai hub gives us the local presence to adapt that experience for UAE and GCC institutions, work closely with their teams and refine the implementation as the regional payments ecosystem develops.
Your team has cited a figure of roughly 640,000 cyberattack attempts a day nationally in the UAE. That figure, from the UAE Cyber Security Council, spans aviation, energy and education as well as financial services, driven partly by regional conflict-related targeting. What’s the actual, narrower number or trend specific to mobile banking fraud that you’d point to instead?
Pushkar Singh: The 640,000 figure describes the UAE’s broader cyber-threat environment across multiple sectors; it is not a measure of mobile banking fraud.
Mobile applications are, however, one of the front doors being targeted by hackers and fraudsters.
The risk is increasingly present inside an otherwise legitimate mobile session. Fraudsters may exploit a compromised device, malicious or remote-control software, screen sharing, overlays or unsafe network conditions.
The financial institution may see valid credentials and a familiar device while the customer’s actions are being observed or manipulated. Attackers are also using automation to adapt more quickly, which makes behaviour and context increasingly important alongside known threat signatures.
For banks, this changes the control model. They need visibility across the application, device and network while the session is active, together with the ability to warn the customer, apply additional verification, block a transaction, or end a high-risk session.
You’ve worked across consulting, telecoms, banking, insurance and government in your career. What’s different about getting a UAE or GCC bank to actually act on a mobile security notice like 2176, versus a bank in India or Europe facing an equivalent requirement?
Pushkar Singh: Banks, fintech companies and other financial institutions do not necessarily wait for regulation to strengthen their security posture. They adopt solutions to protect customers, minimize financial losses and safeguard their reputation.
Regulatory mandates can, however, accelerate execution by giving an issue immediate executive attention, and that is also true in the UAE and other GCC markets.
Several countries in the region have prioritised digital adoption across banking, fintech and government services.
Mobile security is therefore critical to delivering a digital-first economy safely. A key decision for institutions is choosing the right security posture. Protectt.ai brings global best practice to help define mitigation measures for different vulnerability categories, then tailors the approach to the institution’s requirements.
Mobile security is not owned by one team.
Fraud, cybersecurity, compliance, digital banking, mobile engineering and customer operations all have a role. The institution must agree who owns the response, what happens when a risky session is detected, how legitimate customers will be protected from unnecessary friction and how the control will fit within the mobile release cycle.
The emphasis also varies by market.
In India, transaction scale and the speed of mobile payments make performance and rapid enforcement especially important. European institutions may place more weight on established governance, privacy and procurement processes.
In the GCC, banks expect close local engagement and a solution that reflects their regulator, operating model and customer journeys. Protectt.ai’s Dubai-based team helps translate requirements into controls inside the application and supports institutions as those controls move into production.
Twelve months from now, what’s the one thing that would tell you Protectt.ai’s GCC expansion is actually working: a specific bank client, a specific volume number or a specific regulatory partnership, rather than sentiment?
Manish Mimani: The clearest measure would be seeing our existing regional clients move into sustained, large-scale production and expand their use of the platform across additional applications or customer journeys.
We already work with several institutions in the region, although we cannot name them publicly. For me, success is not simply signing another client; it is demonstrating measurable, long-term value within regulated financial institutions.
Pushkar Singh: From a regional growth perspective, success would mean building on our presence in the UAE and Saudi Arabia by entering at least one additional GCC market, supported by a live customer deployment rather than simply an agreement or early-stage discussion.
That would demonstrate that we have developed a repeatable regional model that can be adapted to the regulatory and operational requirements of different GCC markets.

Editor’s Take: Manish’s central claim is that a bank can see valid credentials, a recognised device and a real customer and still be looking at fraud, which is why Protectt.ai argues the app, device and session have to be assessed together.
The most concrete part of the interview is his description of the attack: a remote-access tool, accessibility permissions or an overlay on the payment screen, inside an authenticated session. That matches the behaviours security vendors say CBUAE’s April notice targets.
Pushkar’s point that 640,000 counts attacks across all sectors and doesn’t measure banking fraud is accurate, though neither executive offers a mobile banking fraud number to put in its place. The least specific part is the UAE detail: asked how Aani and Jaywan change the picture, Mimani says detection must reflect CBUAE requirements and UAE journeys without naming a UAE-specific threat or control.
The GCC success test rests on clients Protectt.ai can’t name, so what can be checked in 12 months is a live deployment in a third GCC market.