Table of Contents
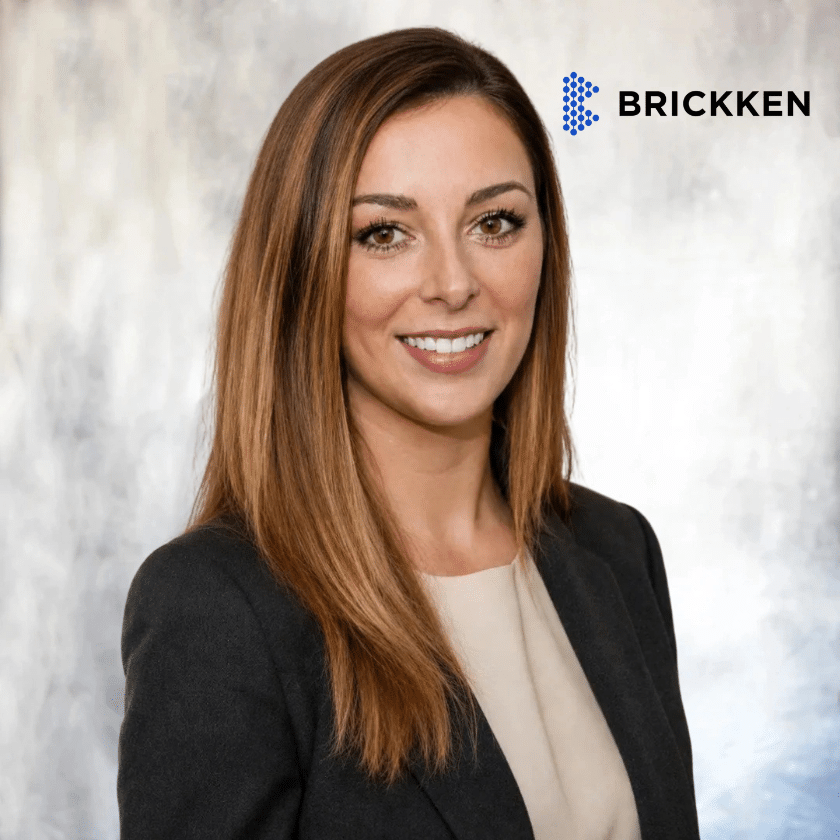
Elisenda Fabrega started her legal career at Applus IDIADA, working on blockchain implementation for autonomous vehicles, before becoming General Counsel at Brickken, where she has spent the past several years building legal and compliance requirements into the tokenization platform’s design rather than reviewing it after the product ships.
Her public track record is almost entirely European, MiCA, the European Blockchain Sandbox, MiFID II, so when the comparison came up between the EU’s regulatory approach and Abu Dhabi Global Market’s, we asked her directly how much of that view is lived experience versus an informed outside read, before getting into the comparison itself.
Brickken, the Barcelona-based tokenization infrastructure provider, closed a €3 million pre-Series A round in April 2026 at a €38 million valuation, and serves more than 150 clients across 30-plus countries with over $500 million in tokenized assets.
We asked Fabrega what ADGM actually gets right that MiCA doesn’t, what tips a tokenization company’s licensing decision, and which part of today’s regulatory frameworks is likely to get tested first as institutional on-chain finance grows.
In Conversation with Brickken’s Elisenda Fabrega on ADGM Vs MiCA
Before Brickken, you worked in blockchain implementation for autonomous vehicles at Applus IDIADA. What pulled you from automotive tech into tokenization law specifically?
Elisenda Fabrega: At IDIADA, I worked in the legal team on emerging technologies: software, electric vehicles, autonomous driving, and distributed ledger technology. During that time, I learned something I found valuable: in technology, how something is designed can directly affect its legal consequences.
For example, who is responsible when an autonomous system fails? Is software a component or a service? Who owns the data generated by a vehicle? These questions can’t always be answered at the end of the process. The answer can depend on decisions that were made much earlier, when the product was being designed and developed.
That experience changed the way I saw the role of a lawyer in technology. If a lawyer only comes in once the product is finished, many of the important decisions have already been made. The lawyer can then explain the legal implications and try to fix any problems, but the room to influence the product is much smaller.
That is what attracted me to Brickken. I had the opportunity to join at an early stage and help build the platform itself, while considering legal and compliance requirements as part of the design process.
So, for me, it was a different way of practising law.
Instead of looking at a finished product and asking, “What is wrong with this?”, you are involved from the beginning, working with engineers and product teams to ask, “How should we build this so that it works both technically and legally?”
And that is the kind of legal work I wanted to do.
How closely have you actually worked with ADGM’s framework day to day, versus observing it from the European side?
Elisenda Fabrega: My work with ADGM has been practical, though not in the sense of working within the framework day to day. Because of the nature of Brickken’s platform, we have analysed ADGM. This has involved working with local counsel and developing written legal analysis around how our business and future commercial objectives would be treated there and what regulatory requirements would apply.
That is quite different from looking at a regulatory framework from the outside simply to understand it. When you analyse a jurisdiction because it has real implications for your platform, you keep coming back to a very practical question: if we were operating there, what would we actually be and what would we need to comply with?
I also found that looking at another jurisdiction this closely changes the way you see your own. When you work within the European framework every day, it is surprisingly difficult to step back and see its structure clearly.
That’s where I found something I hadn’t expected. I initially thought I would be comparing a fragmented European system with a more streamlined framework in the Gulf. Instead, I found a regulatory architecture where securities and Virtual Assets sit within the same broader framework, while still subject to distinct rules and regulatory treatment.
That changed the comparison for me. The interesting question is not simply which jurisdiction has the tidier framework. It is where each jurisdiction draws the line between securities and Virtual Assets/crypto-assets, how that line affects the activities a business can perform, and ultimately how much of that complexity the business has to navigate.
Is MiCA actually making expansion easier for tokenization businesses, or is that still mostly theoretical?
Elisenda Fabrega: Both, but it depends entirely on what you tokenize. And this is where I think the discussion around MiCA often becomes too simplistic. The fundamental distinction remains the same: crypto-assets on one side, tokenized financial instruments on the other. MiCA was designed for the first and stops at the second.
For crypto-assets, the passport is real. A firm authorised in one Member State can provide its services across the Union once its home authority has notified the relevant authorities in the other Member States. That is a significant improvement over twenty-seven separate national regimes, and it is a very practical benefit for firms operating in this space.
The picture changes when you move into financial instruments. If tokenization is done correctly, MiCA does not apply to tokens that represent financial instruments. If the token qualifies, for example, as a digital representation of a transferable security, the relevant framework is instead the applicable financial-services framework, including MiFID II and, where applicable, the Prospectus Regulation and the relevant settlement and custody rules.
The DLT Pilot Regime may also become relevant where the activity falls within its specific scope for DLT market infrastructures.
So the MiCA passport does not cover a core area of tokenization activity. That does not mean there is no passporting at all: MiFID II itself provides a framework for the cross-border provision of investment services. But the regulatory analysis is different, and depending on the activity, structure and jurisdiction, additional national requirements can still become relevant.
There is also a timing point that is easy to overlook. The transitional period could run until 1 July 2026 at the latest, but Member States could shorten it. This meant that firms faced different transition deadlines across the Union. So while MiCA has created a much more coherent framework for crypto-asset services, we are still early in seeing how consistently Member States apply it.
So my honest answer would be: yes, MiCA has made expansion materially easier, but not uniformly across every type of tokenization business. For regulated crypto-asset services, the benefit is direct: there is now a harmonised framework and a passporting mechanism across the EU.
For tokenized financial instruments, the benefit is more indirect. The MiCA passport itself does not apply, and cross-border investment services continue to rely on the MiFID II framework. However, MiCA can still be relevant to the same business or group where it also provides crypto-asset services falling within MiCA. An authorised investment firm may, subject to the applicable conditions, provide certain MiCA-regulated crypto-asset services through the notification mechanism under Article 60.
So in practice, a tokenization business operating across both areas can benefit from a more coherent regulatory architecture: MiFID II for tokenized financial instruments and MiCA for crypto-asset services within its scope. I wouldn’t say everything has suddenly become simple, but compared with a landscape of largely national approaches, MiCA has made European expansion much more tangible rather than merely theoretical.
What does ADGM get right that MiCA doesn’t, in your view?
Elisenda Fabrega: First, I wouldn’t compare ADGM directly with MiCA, because they aren’t really comparable. ADGM is a jurisdiction, with its own courts and its own self contained financial services framework, whereas MiCA is one regulation within the broader European framework.
And when you put ADGM next to the European framework as a whole, there is no particular point where I would say that ADGM gets something right and Europe gets it wrong. Both systems recognise the fundamental distinction between a digital asset that represents a financial instrument and a digital asset that is not.
In ADGM, a token that represents a security is deemed to be a Security by the FSRA, assessed case by case, while virtual assets are treated as commodities and are expressly not Specified Investments, so they are governed by a dedicated chapter of the conduct rules that applies on top of the general rulebooks rather than in place of them. Europe reaches the same division through MiCA on one side and MiFID II and the rest of the financial services framework on the other.
Where I do see a difference is in how the two are structured and experienced in practice. In ADGM that analysis takes place within one jurisdiction, one legal system and one financial regulator. In Europe there are national competent authorities, national options within MiCA itself, divergent supervisory practice, and, for anything that qualifies as a representation of a financial instrument, MiFID II as transposed in each member state on top of twenty seven bodies of securities and property law. That is where a great deal of the time goes.
But I would not necessarily call that a weakness of MiCA. In fact I think MiCA gets something very important right that ADGM cannot replicate in the same way, which is a single harmonised rulebook across the Union.
It is also worth saying that neither framework merges the two bodies of law, and that is visible even within a single company. One issuer on our platform has an existing utility token and has separately tokenized 10 percent of its equity as a distinct instrument. Same issuer, same technology, and in many cases the same holders, but two entirely different bodies of law apply because what separates them is not who supervises the company. It is what the holder actually owns.
So if I had to answer the question directly, I would say that ADGM’s strength is not a fundamentally better classification system. It is that the classification sits within a single jurisdiction and regulatory architecture. Europe’s strength is the harmonised rulebook, although supervision remains national, which is why the Commission proposed to move the authorisation and supervision of crypto-asset service providers to ESMA.
For a tokenization business, therefore, the interesting issue is not which framework has the better label. It is how efficiently you can determine what the instrument legally is, and then apply the right regulatory framework to it.
When a tokenization company is choosing where to license, what actually tips the decision?
Elisenda Fabrega: The order in which these questions arise is fairly consistent, and it actually starts before jurisdiction enters the conversation at all.
The first question is the token’s legal nature. Before choosing a jurisdiction, you need to understand what you are tokenizing and how you are structuring the tokenization so the resulting token has the characteristics you intend. That classification determines much of the regulatory analysis that follows.
The second question is where the company is based, who it is targeting, and which markets it intends to serve. This is where jurisdiction becomes relevant. You need to understand where your clients are and how you intend to provide the relevant services to them, and then assess whether the regulatory framework and authorisation in the chosen jurisdiction actually allow you to conduct those activities in your target markets. Choosing a jurisdiction first and analysing the target market afterwards can leave you with an authorisation that does not properly cover the business you actually want to build.
The third question is how the regulatory perimeter will translate into the company’s day-to-day operations. Having tokenized securities and crypto-assets under a single regulator can certainly be an advantage, but it does not merge the two regulatory frameworks. If a business operates across both areas, its compliance function still has to manage the requirements applicable to each. And that is not simply a cost of obtaining the licence; it is an ongoing operational requirement.
Then come the practical considerations, which in my experience are often what ultimately tip the decision: how long authorisation actually takes, rather than simply what the rulebook says; how predictable and workable the supervisory relationship is; and whether the company can actually establish the banking, custody and other service-provider infrastructure it needs.
Those practical points can determine whether an expansion is viable much faster than a regulatory requirement on paper. A licence is only valuable if it can actually be operationalised.
Ultimately, the right jurisdiction is not necessarily the one with the most attractive rulebook, but the one where the regulatory framework, target markets and operational infrastructure actually work together for the business you are building.
As tokenized securities and institutional onchain finance grow, which part of today’s regulatory frameworks will get tested first?
Elisenda Fabrega: I think the first part to be really tested will be the framework around secondary markets and market infrastructure.
Creating a digital representation of a security is already something the existing regulatory framework can accommodate. The bigger change comes when those assets start moving and trading on-chain at institutional scale.
That is where some of the assumptions built into traditional market infrastructure are going to be tested: how trading venues operate, how custody and settlement work, when a transfer is legally final, and how ownership is recorded when the transaction happens on a blockchain.
I don’t see that as a problem for tokenisation. Quite the opposite. It is the natural next step once tokenised assets move beyond individual issuances and start becoming part of the broader financial market.
The interesting regulatory question is whether we can let that market infrastructure evolve without simply reproducing every layer of the traditional system on a blockchain. If we can preserve the same standards of investor protection and legal certainty while taking advantage of what on-chain infrastructure can actually do, I think that is where institutional adoption will really accelerate.
Editor’s Take: Brickken has analysed ADGM through local counsel for real commercial reasons, which is a genuine, defensible form of expertise, just not the same as operating inside the framework day to day.
The sharpest single point in the interview is the one about a single issuer running both a utility token and separately tokenized equity under two entirely different bodies of law, “what separates them is not who supervises the company. It is what the holder actually owns.” That says more about how tokenization regulation actually works than either ADGM is better or MiCA is better would.
Also, read Tabadulat’s Samy Mohamad on Fixing Disintegration in Shariah-Compliant Investing